The world is changing super fast in 2026, especially because of clever computer programs we call Artificial Intelligence, or AI. These AI programs are changing how countries keep themselves safe.
They are changing how we gather important information, look at it closely, and make sure it’s true. This is where something called SVR intelligence comes in.
SVR intelligence helps us understand the new way information works for national security. SVR stands for Signals, Verification, and AI. It’s all about how these three things come together. Fast AI tools are now used to collect huge amounts of information, sometimes even through autonomous AI systems. These tools also help make sense of all that data quicker than ever before. Even small, powerful computers that use edge AI can now process information right where it is collected, which means faster decisions.
But with all this new AI, there’s a big question: how do we know the information is real and not fake or wrong? This is the "Verification" part of SVR intelligence. Making sure our information is correct is more important than ever. The United States government knows that AI will change national security a lot. They see AI as a transformative technology for national security.
This guide will walk you through what SVR intelligence really means. We will look at how it affects national rules, daily work, and making sure everyone follows the rules. Understanding how to build safe, strong, and honest AI systems for these tasks is key for everyone in this field. You can learn more about AI agent governance building safe compliant advanced AI systems.
For those who want to keep up with the fast-moving world of AI and its rules, it helps to have good information.
Get clear daily AI updates from The AI Newsletter Worth Reading.
Defining SVR intelligence: components, actors, and technical primitives
Now, let’s look closer at what SVR intelligence really means. It stands for Signals, Verification, and Reconnaissance/Response.
Each part works with artificial intelligence (AI) to make national security efforts smarter and faster in 2026.
The Three Parts of SVR Intelligence
- Signals (S): This first part is all about gathering information. Think of it like a giant ear listening to everything. In the past, people collected signals. Now, AI systems can automatically collect huge amounts of data from many places. This includes things like electronic communications, satellite pictures, and data from the internet. AI helps sort through this huge pile of "signals" to find the important bits.
- Verification (V): After collecting signals, the next big step is to check if they are true. This is the "Verification" part. With so much information, it is easy for wrong or fake data to show up. AI helps here by looking for patterns, comparing new data to old, and spotting anything that looks suspicious. Making sure information is correct is vital for making good decisions for national security. Many government groups are working on this, as seen in efforts to promote Harnessing Artificial Intelligence to Fulfill National Security Objectives.
- Reconnaissance/Response (R): This part is about understanding what is happening and then deciding what to do. "Reconnaissance" means looking at a situation very carefully, like scouting. AI helps analyze all the verified information to show clear pictures of threats and opportunities. "Response" is about acting on that understanding. AI can help plan the best actions quickly, whether it’s giving warnings or suggesting specific steps to keep people safe.
Who Uses SVR Intelligence?
Many different groups are involved in using and developing SVR intelligence.
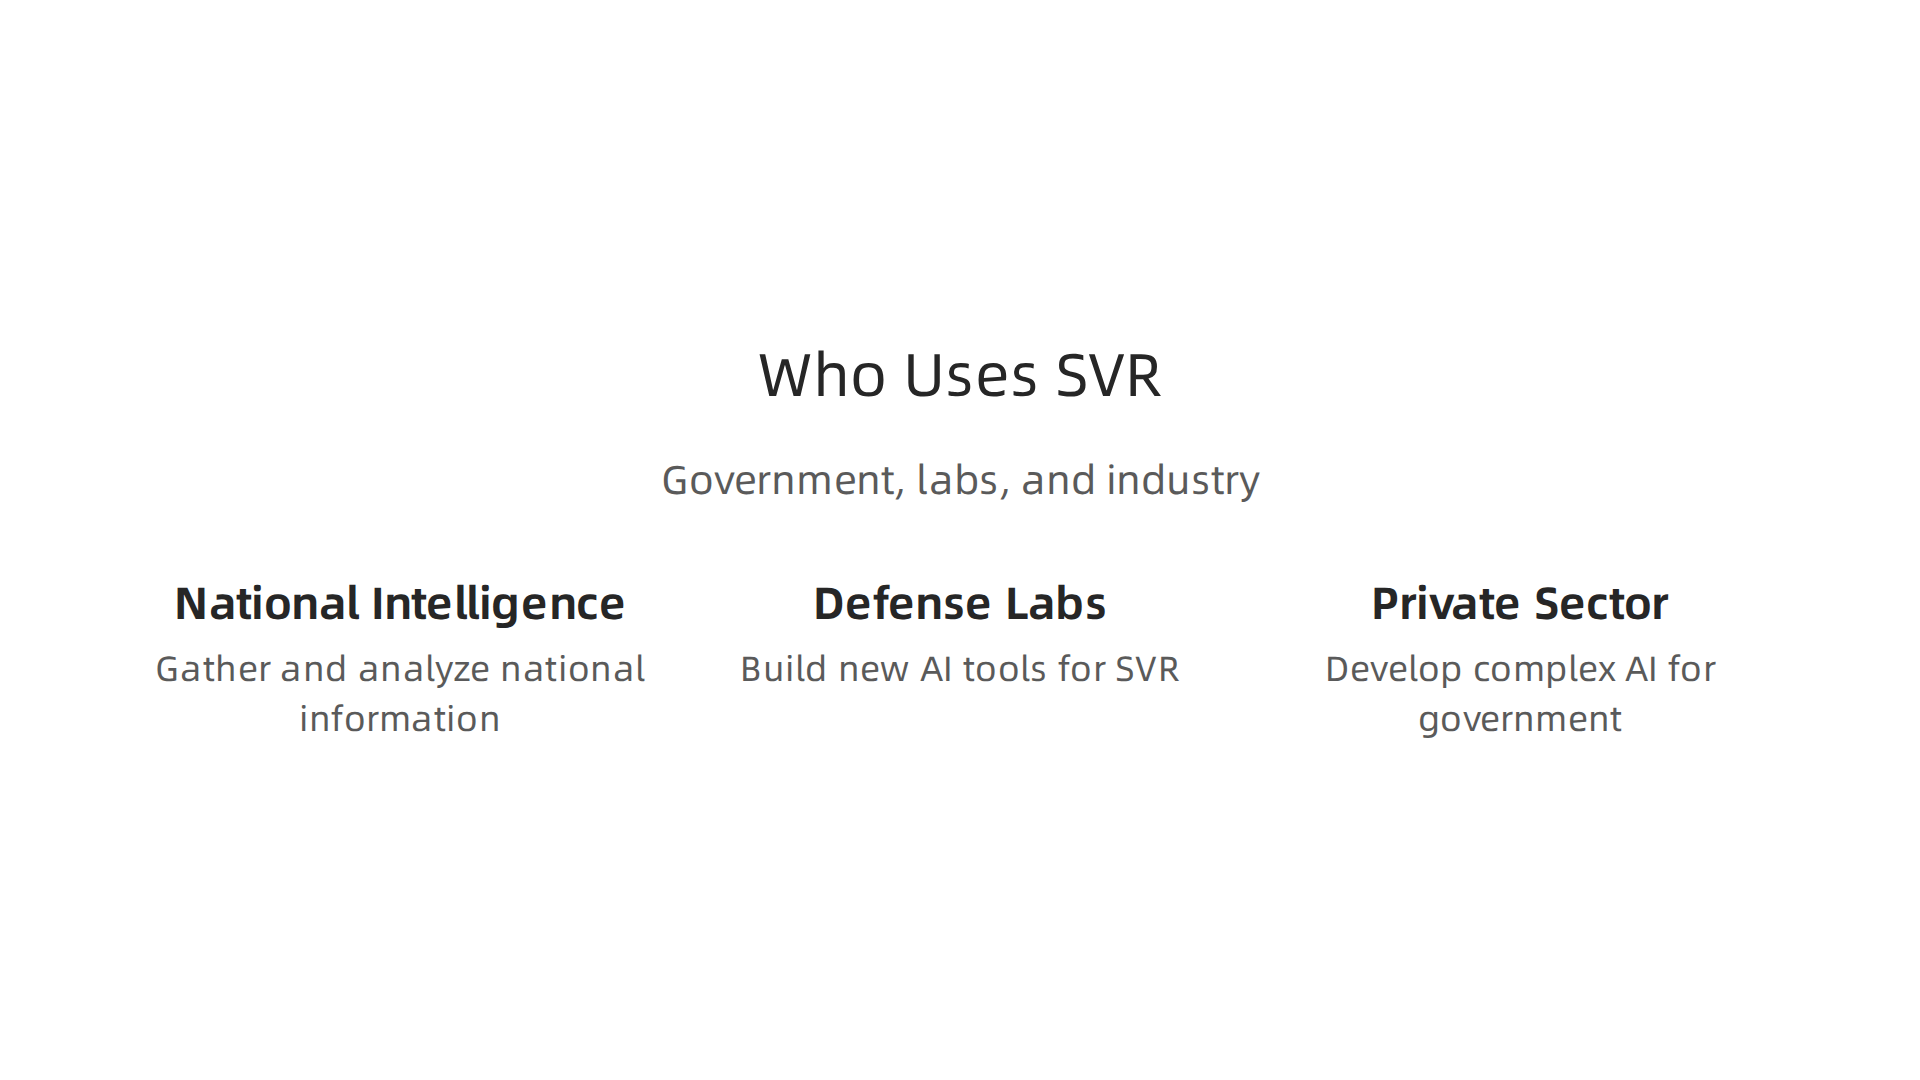
- National Intelligence Bodies: These are groups like the US Intelligence Community. They gather and analyze information to protect the country. They use SVR intelligence to get a clear picture of dangers from other countries or groups.
- Defense Labs: These labs, like those working with the Department of War, build new tools and technologies. They are at the front of making AI systems that can help with SVR tasks. The goal is to make sure America’s defenders have the best and most secure AI systems. For example, the Department of War has its own Artificial Intelligence Strategy for the Department of War to guide its efforts.
- Private-Sector Providers: Many private companies that create advanced AI also work with the government. They develop the complex AI tools and software that make SVR intelligence possible. This partnership helps bring the newest technology into national security uses.
The way information flows between these groups is very important. It needs to be fast, accurate, and super secure. They work together to build strong systems for national security in 2026. Learning how to build AI securely and compliantly is key for everyone involved.
To make SVR intelligence work, many technical pieces must come together. These are like the building blocks that let AI help with national security. We’re talking about smart computer programs, how data moves around, and special tools to check if information is real.
Machine Learning Models and Data Fusion
At the heart of SVR intelligence are machine learning (ML) models. These are computer programs that can learn from data without being told exactly what to do. They are very good at spotting patterns in huge amounts of information.
For the "Signals" part of SVR intelligence, ML models help gather and sort data from many places. This data can be anything from radio waves to social media posts. The models learn what’s important and what’s just noise.
A big part of this is called "sensor fusion." Imagine you have many different eyes and ears gathering information: cameras, radar, microphones, and other sensors. Sensor fusion is when we combine all this information into one clear picture. AI models are excellent at this. They can take data from different types of sensors and put it together to give a much better understanding than any single sensor could on its own. For example, ML helps combine various sensor inputs to improve tasks like identifying objects in real-world settings A Survey of the Multi-Sensor Fusion Object Detection Task in … – PMC. This is very important for autonomous AI systems, which need to understand their surroundings to make decisions on their own, especially in national security or remote operations where data might come from distant places, sometimes using edge AI devices.
Different machine learning methods are used here, like deep learning, which is good for looking at pictures and sounds, and other methods for making sense of complex data streams A survey on machine learning for data fusion. They all work to make the incoming signals useful.
Data Pipelines
Think of data pipelines as the superhighways for information. They are systems that move data from where it’s collected to where it needs to be analyzed by ML models, and then to the people who use it. These pipelines need to be fast, secure, and able to handle huge amounts of data quickly. If data doesn’t flow smoothly, the whole SVR intelligence system slows down. Keeping these systems secure is a major focus for everyone involved.
Verification Tooling
Once data is collected and processed, we need to make sure it’s true. This is where verification tools come in.
- Provenance: This means knowing where the data came from. Like knowing the full history of a product, provenance for data tells us its origin, who touched it, and how it was changed along the way. Without proper data provenance, it’s hard to trust the information, especially when dealing with complex data sources PROVENANCE IN FUSION.
- Authentication: This is about proving that the data is real and hasn’t been faked or tampered with. It’s like checking someone’s ID. As AI gets better, it can create very convincing fake data, sometimes called deepfakes, which makes authentication much harder in 2026. New solutions are always being developed to check for fake data Developing new solutions for data provenance and deepfake ….
- Adjudication: This is when different pieces of information might conflict, and we need to decide which one is correct. AI can help compare different data points and flag areas where things don’t match up, making it easier for human experts to make the final call.
AI introduces new challenges here. Because AI systems can generate data, it can be tough to know if the data itself is honest, even if it’s technically secure. Ensuring svr intelligence systems can effectively verify information is critical for their reliability and trust in national security applications. Organizations like the CDC, which relies on accurate data for public health, also face significant challenges in data verification, making "cdc artificial intelligence" efforts critical for trustworthy health insights.
The previous section ended discussing how important it is to verify data for svr intelligence systems, especially with new challenges like deepfakes. Now, let’s look at the good and bad sides of using AI in these important systems.
Operational benefits and risks: speed, scale, bias, and adversarial vulnerabilities
Using AI in svr intelligence brings many big advantages. One of the best things is speed. AI can look at and understand huge amounts of information much faster than people can. This means we can find important signals or threats very quickly. Imagine trying to sort through millions of security camera feeds or internet conversations by hand. AI can do it in seconds.
AI also helps with multi-source correlation. This means putting together clues from many different places. For example, if a security camera sees something, and a listening device hears something, AI can connect these pieces of information to form a clearer picture. It’s like having many detectives working together at lightning speed, each sharing their findings instantly. This helps make better predictions about what might happen next.
But with these great benefits come serious risks.
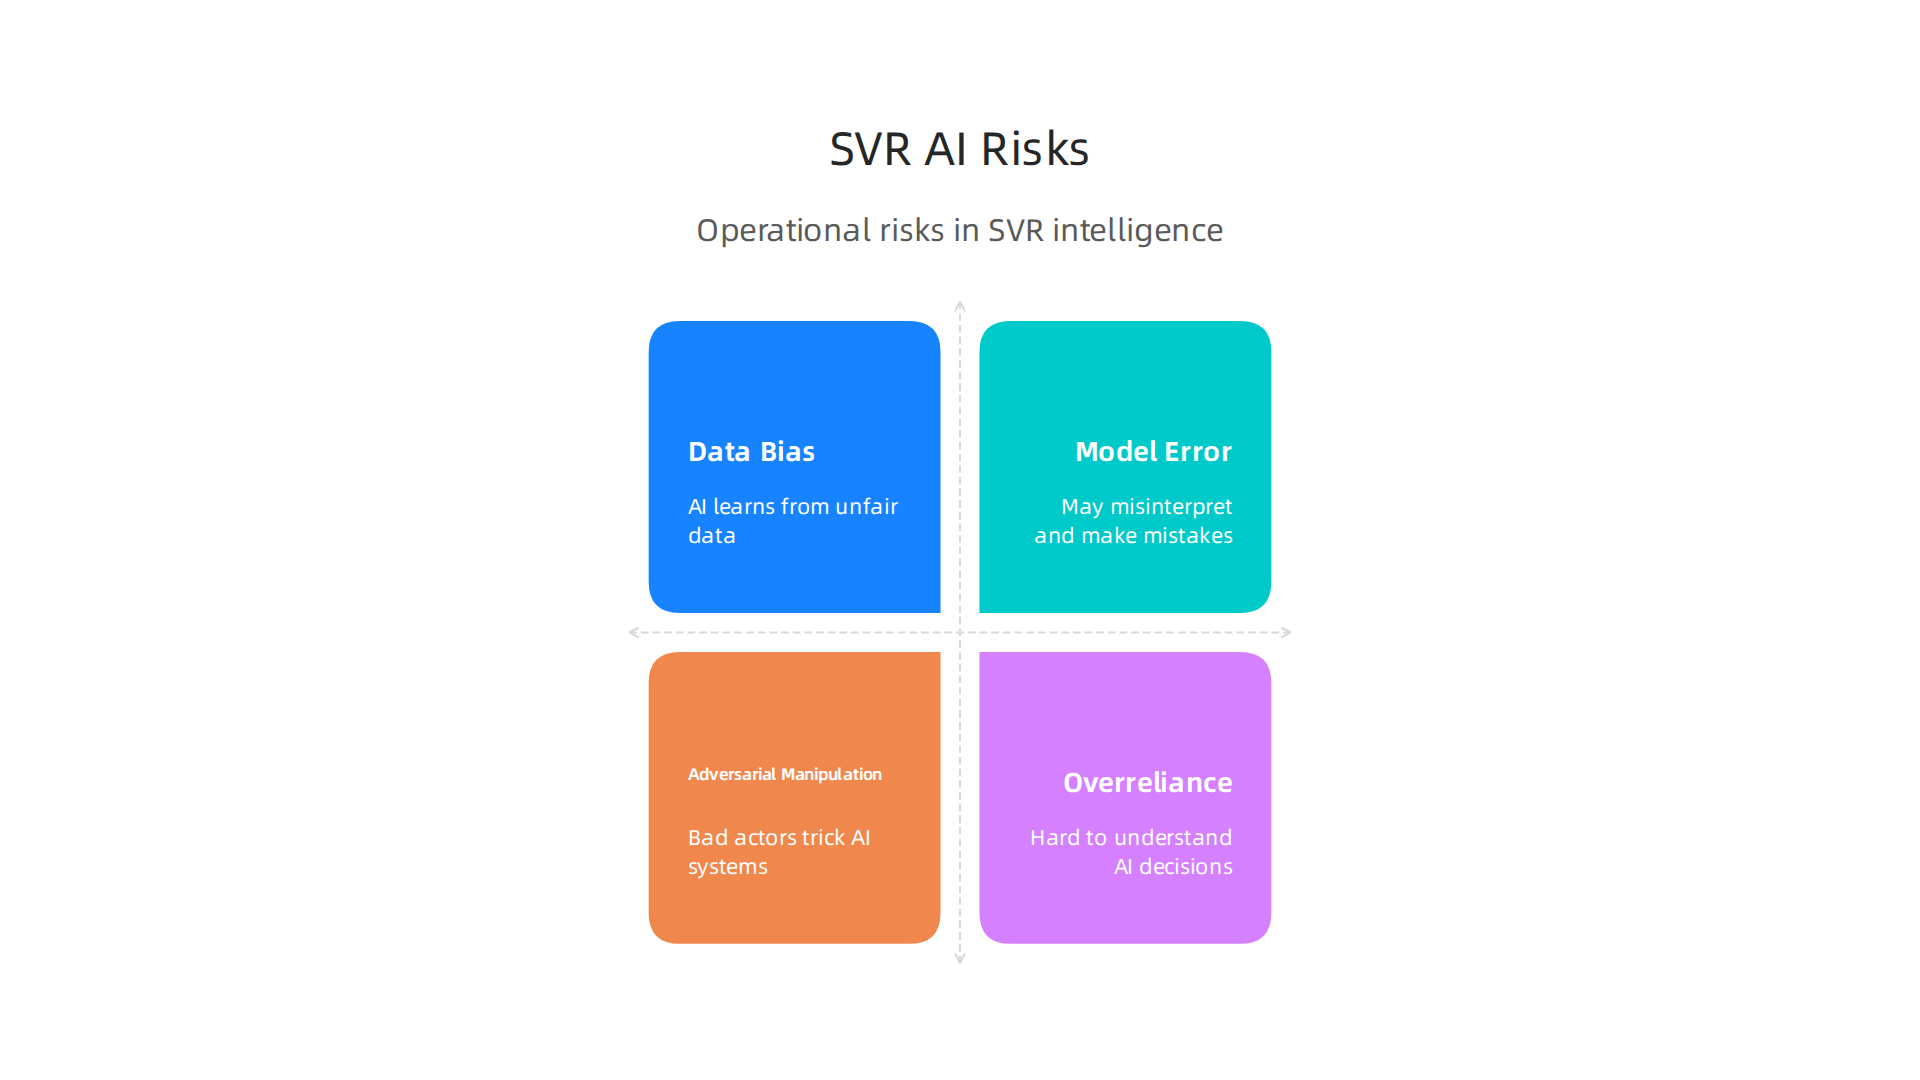
- Data Bias: AI learns from the data it’s given. If this data is not fair or has old prejudices, the AI will learn those biases too. This can lead to unfair decisions or wrong predictions. For example, if an AI is trained mostly on data from one type of area, it might not work well in a different area. It’s like teaching a child only one side of a story; they won’t have a full understanding.
- Model Error: Even the best AI models can make mistakes. Sometimes they might misinterpret something, or just not understand a new situation they haven’t seen before. These errors can have serious consequences in national security.
- Adversarial Manipulation: This is a tricky risk. Bad actors can try to trick AI systems on purpose. They might feed the AI bad data or make small changes that humans wouldn’t notice, but that can make the AI give wrong answers. This is called an adversarial attack, and it’s a growing concern in 2026 for AI systems, making it harder to trust their outputs sometimes. The National Institute of Standards and Technology (NIST) has published a report on Adversarial Machine Learning: A Taxonomy and Terminology of Attacks and Mitigations. Dealing with these kinds of attacks is a big part of making AI systems safe and reliable, as they introduce new security threats throughout the AI model’s life cycle Cybersecurity Opportunities and Risks of Artificial Intelligence in ….
- Overreliance on Opaque Systems: Sometimes, AI systems are like "black boxes." We can see what goes in and what comes out, but it’s hard to understand exactly how the AI made its decision. This lack of clear understanding can make it hard for humans to trust the AI or to fix problems when they arise. It also means we might rely too much on AI without truly understanding its limitations. Experts are pushing for more ways to explain how AI makes decisions, especially in critical applications like in A Survey of Multi-sensor Fusion Perception for Embodied AI.
Managing these risks is very important for making sure svr intelligence stays helpful and doesn’t cause new problems. Building secure AI systems requires a clear understanding of potential threats and how to protect against them. You can learn more about this by exploring resources on how to build AI securely and compliantly. Organizations and governments are working hard on rules and guidelines to make AI safe, as highlighted in reports like the 2026 International AI Safety Report, which talks about general-purpose AI risks including malicious use and malfunctions International AI Safety Report 2026.
When we talk about using AI in svr intelligence, just like we talked about risks, it’s super important to have clear rules. Think of these rules as guiding rails that keep AI systems safe and fair.
These rules come from laws and special groups that watch over how AI is used.
Legal Rules for AI in Intelligence
Even with all the good things AI can do, we must make sure it doesn’t step on people’s rights. There are already laws that protect things like your personal information and your freedom. Using svr intelligence tools that have AI must follow these rules very strictly.
For example, privacy laws make sure that AI doesn’t collect or share too much of your personal data without a good reason. And civil liberties mean that AI should not be used in ways that are unfair to certain groups of people or that limit their freedoms. In 2026, many places are working on new laws specifically for AI. The Council of Europe, for instance, has created the first international legal agreement to make sure AI respects human rights, democracy, and the rule of law The Framework Convention on Artificial Intelligence. Also, the UN has talked about how AI must follow human rights laws, especially when used in things like fighting terrorism Protecting Human Rights while.
Another big area is export controls. This means there are rules about sending very powerful AI technology or "autonomous ai" systems to other countries. The US Commerce Department, for example, has put rules on sharing advanced AI models, making sure they don’t fall into the wrong hands Commerce Department Extends Export Controls to Advanced AI Models. This is to protect national security.
Watching Over AI and Holding It Accountable
Since AI is so new and powerful, we need special ways to watch over it. This is called oversight. Governments and other groups are setting up systems to make sure AI is used safely and correctly.
Here are some ways they are doing this:
- New Laws: In the US, states like Colorado are bringing in their own AI acts in 2026. These laws require companies using "high-risk" AI systems to check for problems and tell people about how their AI works AI Legal Watch: January 2026. The US government is also setting up ways to check advanced AI models before they are widely released Promoting Advanced Artificial Intelligence Innovation and Security.
- Evaluation Frameworks: Groups are building special tools to test how safe and fair AI systems are. For example, Cisco has shared a new way to check AI systems for cybersecurity threats Cisco Launches Open Source Foundry Security Spec to…. These frameworks help us understand how well AI is working and if it has any weak spots.
- Accountability: This means someone needs to be responsible when an AI system makes a mistake or causes harm. It’s not enough for an AI to just "do its job"; there needs to be a clear process for fixing issues and holding people or organizations responsible. Many of these rules also apply to edge ai systems, which are AI tools working on devices without needing a constant internet connection, as they also process sensitive information.
There’s a lot of work being done to create a global comparison of AI regulations to see how different countries are handling this. It’s a big puzzle to put together, but it’s very important for keeping AI safe and trustworthy, especially in crucial areas like svr intelligence. Learning more about AI agent governance can help you understand how these complex systems are managed.
We’ve talked about the rules and watching over AI systems. Now, let’s think about how we can actually check if what these AI systems tell us is correct and trustworthy. This is especially true for svr intelligence systems. We need clear ways to measure and prove that AI outputs are good. This is where standards, metrics, and evidence come in.
Key Ways to Check AI Outputs
To truly trust AI, especially in sensitive areas, we need to look at a few important things:
- Provenance: This is about knowing exactly where the AI’s information came from. Think of it like a detective checking the source of a clue. Was the data gathered fairly? Is it up-to-date? For svr intelligence, knowing the origin of every piece of data used by an AI is vital to ensure its reliability and prevent misinformation.
- Confidence: How sure is the AI about its own answers? AI models should tell us how confident they are in their predictions or findings. If an AI system says something with low confidence, it tells us to double-check that information. This is really important when using AI for big decisions.
- Reproducibility: If you run the same AI system with the same information again, does it give you the same answer? If an AI system gives different answers each time, it’s hard to trust. Reproducibility means we can get the same results over and over, which helps us believe the AI is working correctly. This is a critical factor for any system, including those working as autonomous ai or edge ai, to ensure consistent performance.
- Interpretability: Can we understand how the AI got its answer? Sometimes AI systems work like a "black box," giving an answer without showing their steps. For important tasks, we need to see the logic. Being able to explain the AI’s reasoning helps us find mistakes and build trust. Researchers are developing frameworks to help evaluate the security and behavior of AI systems, like the AVISE framework for identifying vulnerabilities in AI models and systems AVISE: Framework for Evaluating the Security of AI Systems. Another example is the Jo.E framework which helps coordinate AI evaluations to assess comprehensive AI safety Jo.E: Joint Evaluation Framework for Comprehensive ….
A Simple Plan for Checking AI
Policy and compliance teams need a clear way to check AI outputs. Here’s how they can do it:
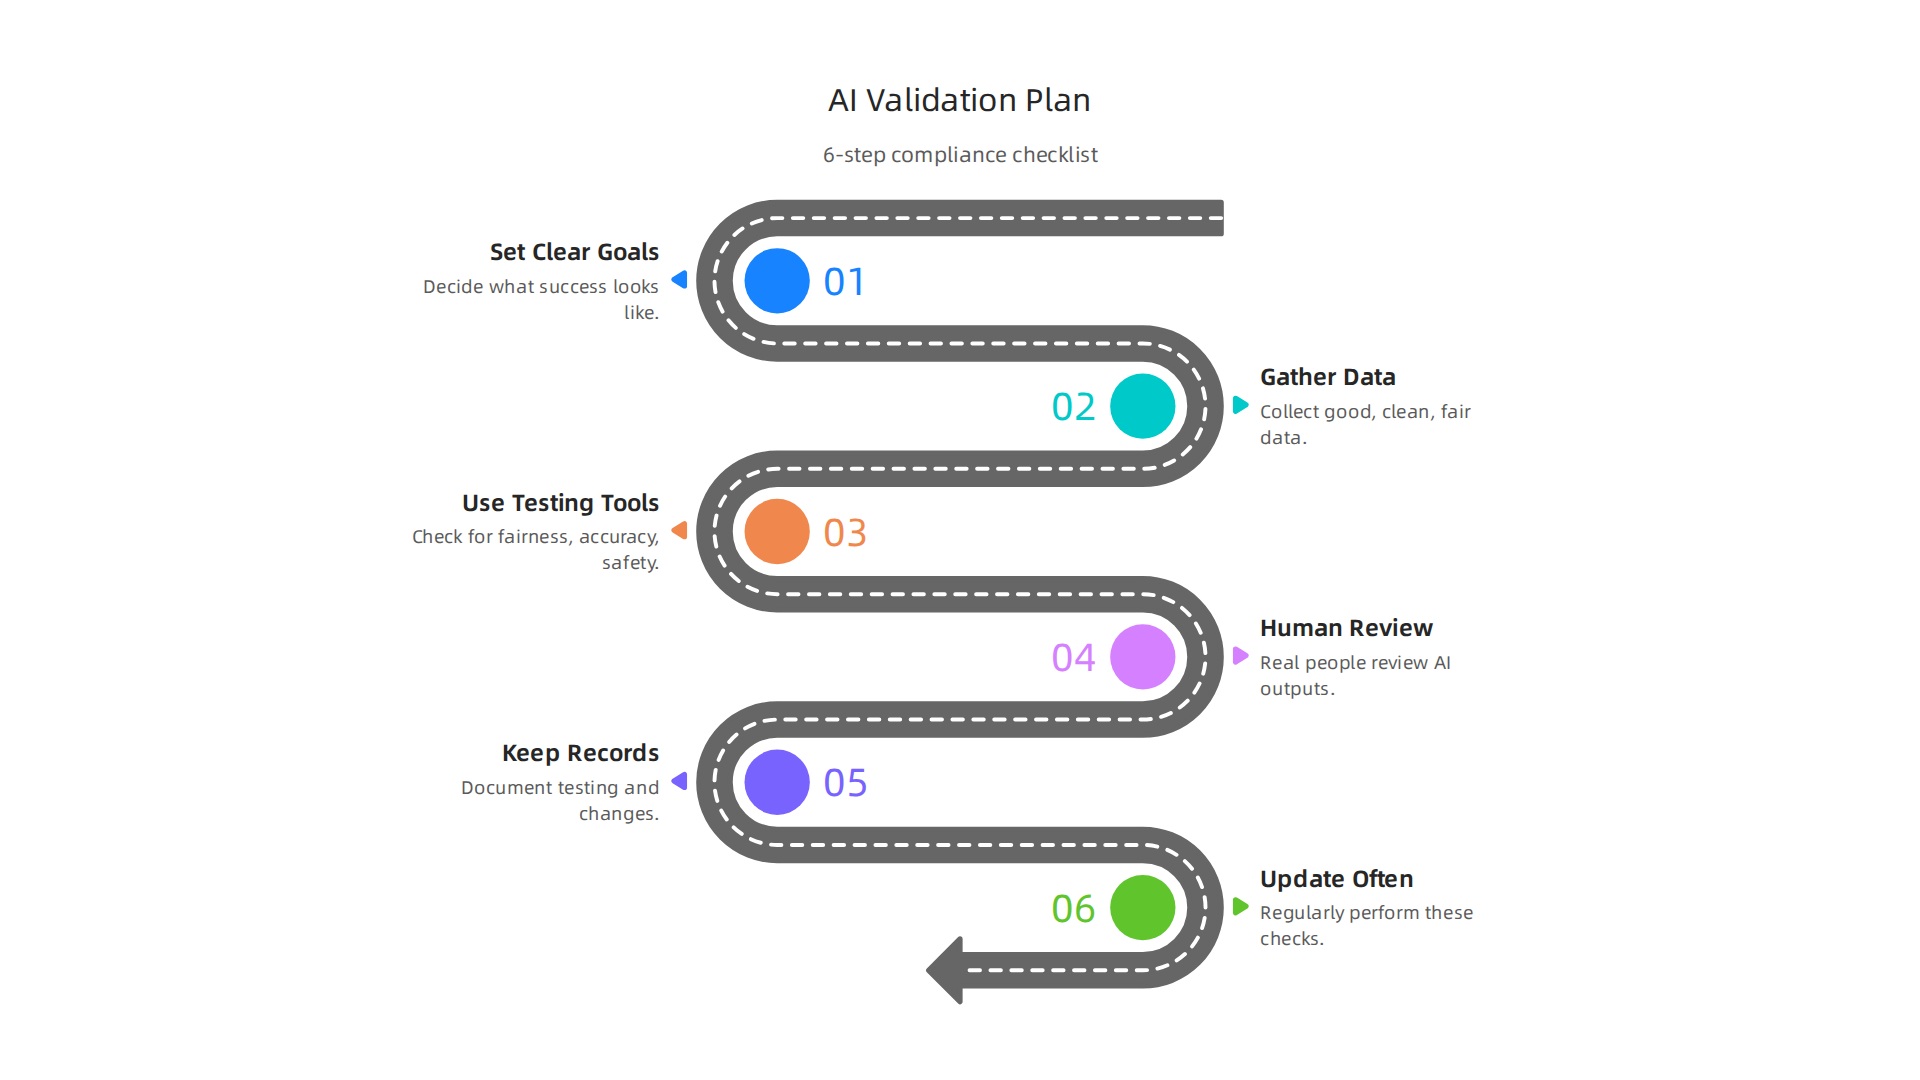
- Set Clear Goals: Before starting, decide what success looks like for the AI. What specific tasks should it do, and how well?
- Gather Data: Collect good, clean data for the AI to learn from and to test it with. Make sure this data is fair and does not have biases.
- Use Testing Tools: Just like we test cars for safety, we need tools to test AI. Many new frameworks are coming out in 2026 to help test things like cybersecurity threats in AI models. These tools check for fairness, accuracy, and safety.
- Human Review: Always have real people review what the AI says or does. Especially for svr intelligence, a human expert should always be the final check. This is important for "high-risk" AI systems where mistakes could cause big problems. Even the CDC might use human review for its cdc artificial intelligence initiatives to ensure public health recommendations are sound.
- Keep Records: Write down how the AI was tested, what happened, and any changes made. This helps to show how trustworthy the AI is over time.
- Update Often: AI systems and the world around them change quickly. So, these checks should happen regularly. New laws and guidelines, like those covered in the 2026 AI Compliance: Upcoming Laws Every Organization Needs to … report, mean that keeping up with changes is key for any organization using AI.
Using these steps helps make sure that AI tools, whether they are complex svr intelligence platforms or simple edge ai devices, are working as intended and can be trusted. Understanding how these systems get their information is part of what it means to truly trust AI. You can learn more about how to ensure AI systems are built with security and compliance in mind by reading our guide on how to build AI securely and compliantly.
Now that we understand how important it is to trust AI and know where its information comes from, let’s talk about what people in charge can actually do. This means leaders, legal teams, and buying departments need clear steps to manage AI systems. They want to lower risks while still getting all the good things AI can offer. This is especially true for svr intelligence systems where decisions can have a big impact.
How to Manage AI Systems in Practice
Taking practical steps to govern AI helps keep things safe and working well.
-
Checking AI Vendors Carefully: When you buy or use an AI tool from another company, you need to be very careful. Ask them about their AI’s security, how they test it, and if it follows the rules. This is like checking a car’s safety record before you buy it. For AI systems, especially complex ones used for svr intelligence, knowing the vendor’s practices helps prevent problems later. You need to identify supply chain risks and how they are handled, as these can introduce vulnerabilities into AI and machine learning systems Artificial intelligence and machine learning: Supply chain risks and ….
-
Setting Up Audit Rules: You should have clear rules that allow you to check the AI system regularly. These "audit clauses" in contracts make sure you can look under the hood and see how the AI is performing. It’s not a one-time check; continuous monitoring is key. The "International AI Safety Report 2026" talks about how important it is to manage risks from general-purpose AI through ongoing testing and evaluation International AI Safety Report 2026.
-
Planning for Problems (Incident Response): Even with the best checks, things can go wrong. What if an AI makes a big mistake, or worse, if someone tries to trick it? You need a plan for these "incidents." This plan should include how to spot weird behavior, how to fix it, and how to learn from it. For example, autonomous AI systems need robust incident plans because they make decisions on their own. Adversarial attacks, where bad actors try to confuse AI, are a real risk that needs plans for defense Cybersecurity Framework Profile for Artificial Intelligence.
-
Controlling Operations for Different AIs:
- For edge AI devices, which work on their own right where they are used (like smart cameras), controls might focus on keeping them secure from physical tampering and making sure their data is private.
- For larger systems, like those used by the CDC, known as cdc artificial intelligence initiatives, controls would involve strict data privacy, ensuring fairness, and making sure human experts always have the final say on health advice.
- And for svr intelligence, which often deals with sensitive information, strict access controls and constant checks for unusual patterns are vital.
Having these kinds of governance, careful buying processes, and smart ways to run AI systems helps organizations feel more secure. It lets them use the power of AI while keeping risks low. To truly navigate the complex world of AI, understanding global tech policies is also a big help. You can read more about it in our guide on navigating global tech systems policy in 2026.
Stay informed about the fast-changing world of AI and technology policy.
The AI Newsletter Worth Reading
Summary
This article introduces SVR intelligence — a 2026 framework combining Signals, Verification, and Reconnaissance/Response — and explains how AI reshapes national-security information workflows. It covers the technical primitives (machine learning, sensor fusion, data pipelines), the verification challenges of provenance and deepfakes, and the operational trade-offs between speed and new vulnerabilities like bias and adversarial manipulation. The guide also outlines the legal and oversight context, including privacy, export controls, and evaluation frameworks, and it gives practical governance steps for procurement, vendor audits, incident response, and testing. After reading, practitioners will understand how to design, verify, and govern SVR AI systems that are faster, more reliable, and legally compliant.