Why ‘Reimagine Home AI’ Matters Now
Imagine a world where your home truly understands you. It’s not science fiction anymore.
In 2026, artificial intelligence (AI) is no longer just in big computer labs. It’s moving into our everyday things, especially in our homes. This shift is why we need to "reimagine home AI" and think about what it really means for how we live and work.
Powerful AI tools, like the smart brains behind programs such as Slack AI and ChatSonic AI, are now being built into smaller devices. Think about your smart speakers that answer questions, your security cameras that watch over your family, or your thermostat that learns your favorite temperature. These are all examples of AI at work right where you live. This idea of AI working on devices themselves, instead of always needing a big cloud computer far away, is called "enterprise edge deployments." It means our home devices are becoming much smarter on their own. Businesses are constantly looking for the best AI for research to improve how these systems work, using advanced ideas like "agentic AI frameworks" to make devices even more helpful and independent.
But with all this amazing new technology comes important questions. As AI helps us "reimagine home AI," we also have to think about some big challenges. How do we keep our personal information private when devices are always listening or watching? How do we make sure our smart home devices are secure and safe from hackers? And what about the rules? Governments around the world are busy creating regulations to keep us safe. For example, a key standard helps make sure connected products, including those with AI, are safe for consumers Connected Consumer Products Standard Revised – ASTM. Also, countries are bringing in rules for smart devices to boost security, like the Cyber Security (Security Standards for Smart Devices) Rules 2025 that began in March 2026 Security Standards for Smart Devices – Department of Home Affairs.
For businesses and professionals, understanding these new rules is very important. They need to think about privacy, security, and the different business choices that come with using AI in our homes. Getting this right means building trust with people who use these devices. It’s about finding a balance between making things smart and keeping them safe. Learning how to build AI securely and in line with rules is a must for any company today. For more on navigating these challenges, understanding AI infrastructure 2026: Navigating cost, security, and compliance is key.
Stay ahead of the curve and get crucial daily insights into AI and technology policy.
The AI Newsletter Worth Reading
When we talk about new rules for home AI, it’s really about how we can build these smart systems so they keep our personal information safe. To truly reimagine home AI, businesses need to think about different ways AI works inside our devices and what that means for privacy. This is where architectural patterns come into play.
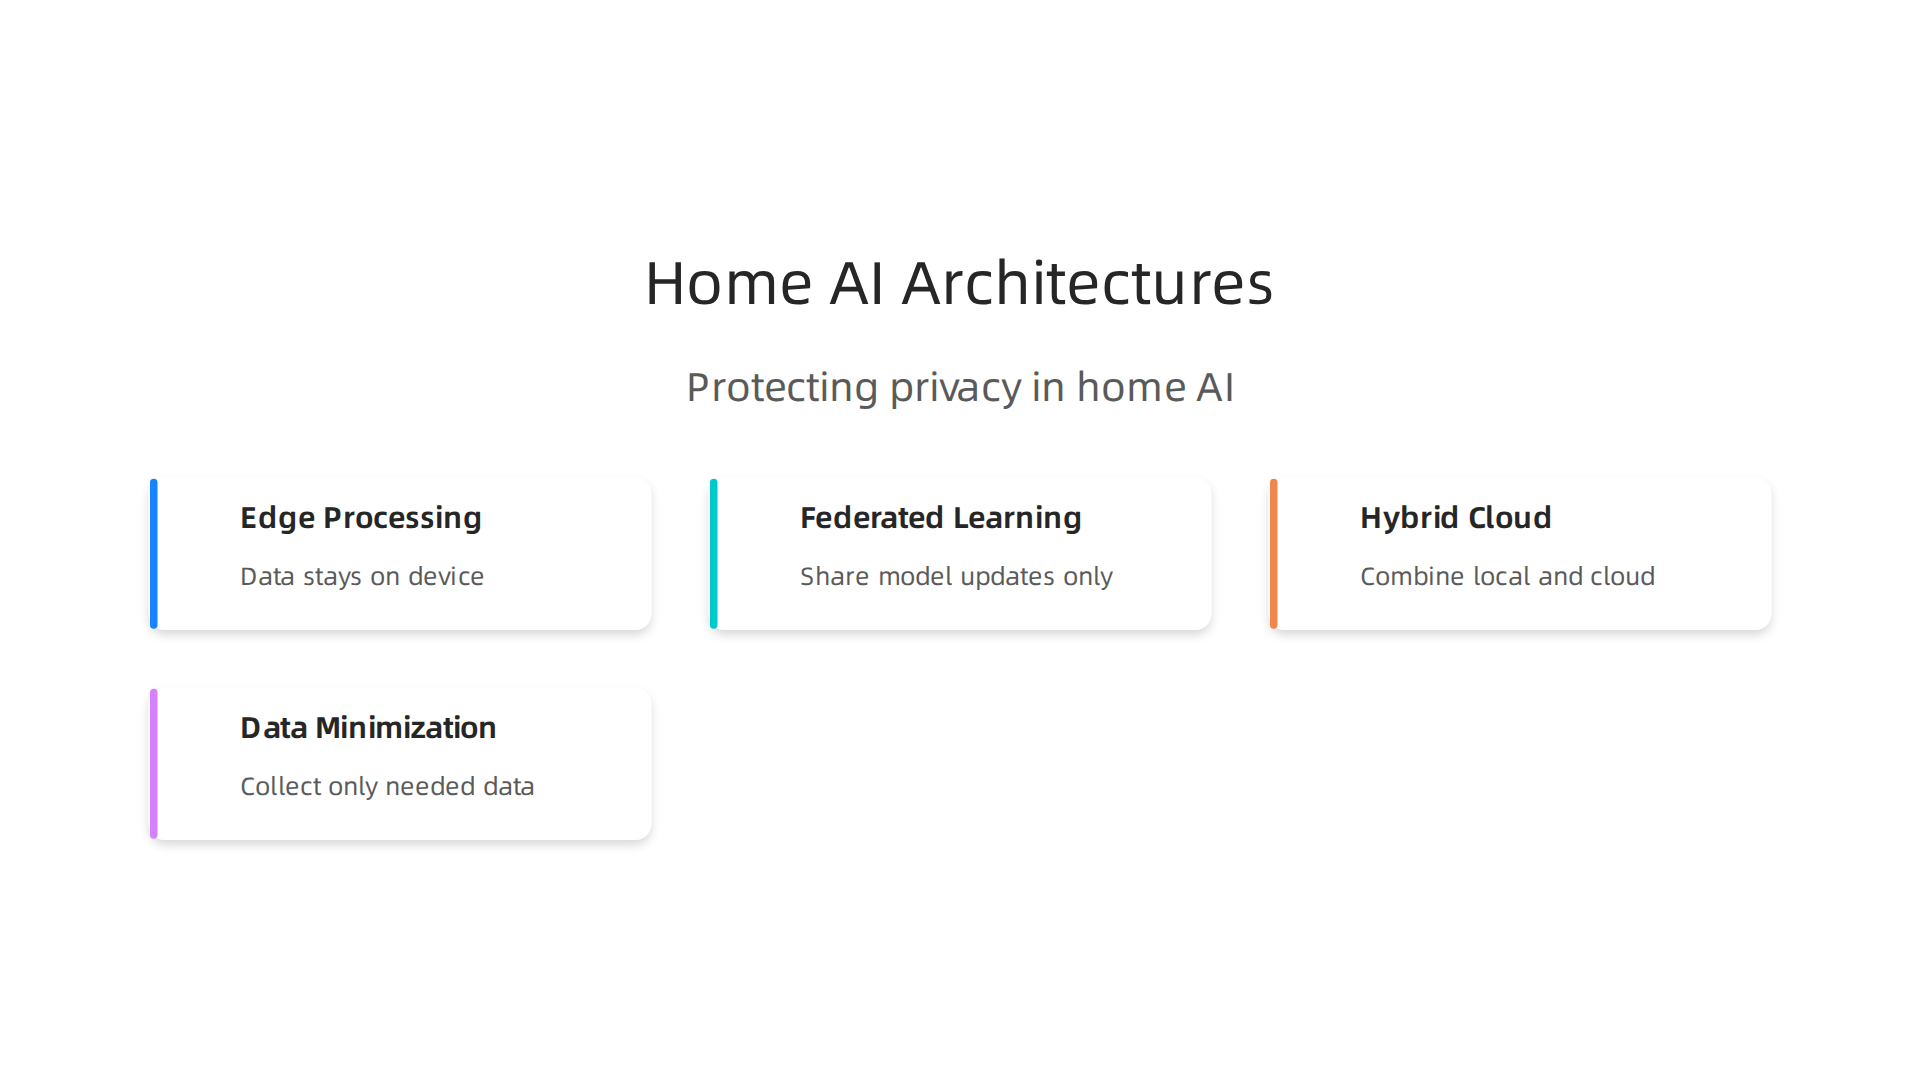
One way to keep your data private is through on-device edge processing. This means the AI brain works right on your smart home device itself, like a smart speaker or camera. The important thing here is that your raw personal data, like your voice or video, stays on that device. It doesn’t get sent to big computers in the cloud far away. This kind of setup gives the highest level of privacy because your sensitive information never leaves your home device A privacy protection approach in edge-computing based on maximized dnn partition strategy with energy saving – Journal of Cloud Computing. It’s like having a very smart helper who only knows what happens in your house and doesn’t tell anyone else.
Another approach is called federated learning. Imagine many smart home devices learning from their own data, but instead of sending all that data to a central place, they only share what they’ve learned in a general way. The main data stays on each device. This method helps create privacy-preserving AI models in smart homes because individual information isn’t exposed Federated Meta-Learning for Privacy-Preserving AI in Smart …. It’s a way for all devices to get smarter together without sharing your personal secrets.
Then there’s the hybrid cloud model, which often involves training AI in the cloud but then running the smart part, called "inference," right on your device. This means the powerful learning happens off-site, but the actual decisions and actions by the AI happen in your home. This approach boosts data privacy because the device handles local tasks without always needing to talk to the cloud Journal of Research and Review: Machine Learning ….
No matter which method companies use, data minimization is key. This means they should only collect the smallest amount of information needed for the AI to work. Less data means less risk. This also helps meet rules and makes people feel safer. To learn more about how AI systems are built and managed, understanding AI Neural Network Architectures Driving Policy, Tech, and Strategy is useful.
Beyond technical solutions, transparency and user consent are super important. People need to know when AI is involved and how their data is used. Companies should clearly show where AI is being used Design Disclosure, Consent and Data-Provenance UX – BXUP and ask for permission in a simple, clear way AI Data Consent: UX Trust Patterns | UX/UI Principles. Sometimes, this means asking for permission just when it’s needed, which is known as progressive consent Progressive Consent & Communication (PCC) – Agentic Design. This way, you stay in control. By thinking about these privacy-first designs, businesses can build trust and make sure their home AI products follow the rules, helping us all truly reimagine home AI for the better in 2026.
Policy and Compliance Landscape: Navigating Cross-Jurisdiction Rules for Home AI
When we talk about how to reimagine home AI to be better and safer, it’s super important to understand all the rules.
In 2026, many countries are making new laws for smart home devices that use AI. Companies need to know these rules to make sure their products are legal and trustworthy, no matter where they are sold.
There are a few main types of rules that matter for home AI:
- Consumer Protection: These rules are about keeping you safe. They make sure products work as promised and don’t harm people. For example, in Europe, the General Product Safety Regulation (GPSR) now covers products that use AI, ensuring they are safe for users The General Product Safety Regulation and AI-Enabled Consumer Products. Also, standards from groups like ASTM International have been updated to include AI guidance for connected products Connected Consumer Products Standard Revised – ASTM.
- Privacy Laws: These laws protect your personal data, like your voice recordings or video feeds. Every country can have different rules about how AI can collect, use, and store your information. For instance, the UK’s Information Commissioner’s Office (ICO) has given clear advice for smart devices about how to handle personal data under GDPR ICO Publishes Finalised Guidance on Consumer IoT Products and Services.
- Product Safety and Cybersecurity: These rules focus on making sure smart devices are secure from hackers and don’t have flaws that could put your home at risk. Many places are bringing in new standards for cybersecurity. For instance, draft regulations in Europe, like ETSI EN 304 632, spell out security rules for smart home products that have security features like smart door locks and cameras EU smart home security regulation. Australia also has new cyber security standards for smart devices that started in March 2026 Factsheet – Security standards for smart devices.
- Interoperability: This is about how well different smart devices work together. While not as strict as privacy or safety rules yet, future policies might push for devices from different companies to connect more smoothly. This is a big part of making home AI truly useful for everyone.
Checklist for Navigating Global Home AI Rules
For companies building home AI, keeping up with these rules can be tricky. Here’s a simple checklist to help teams handle compliance across different places:
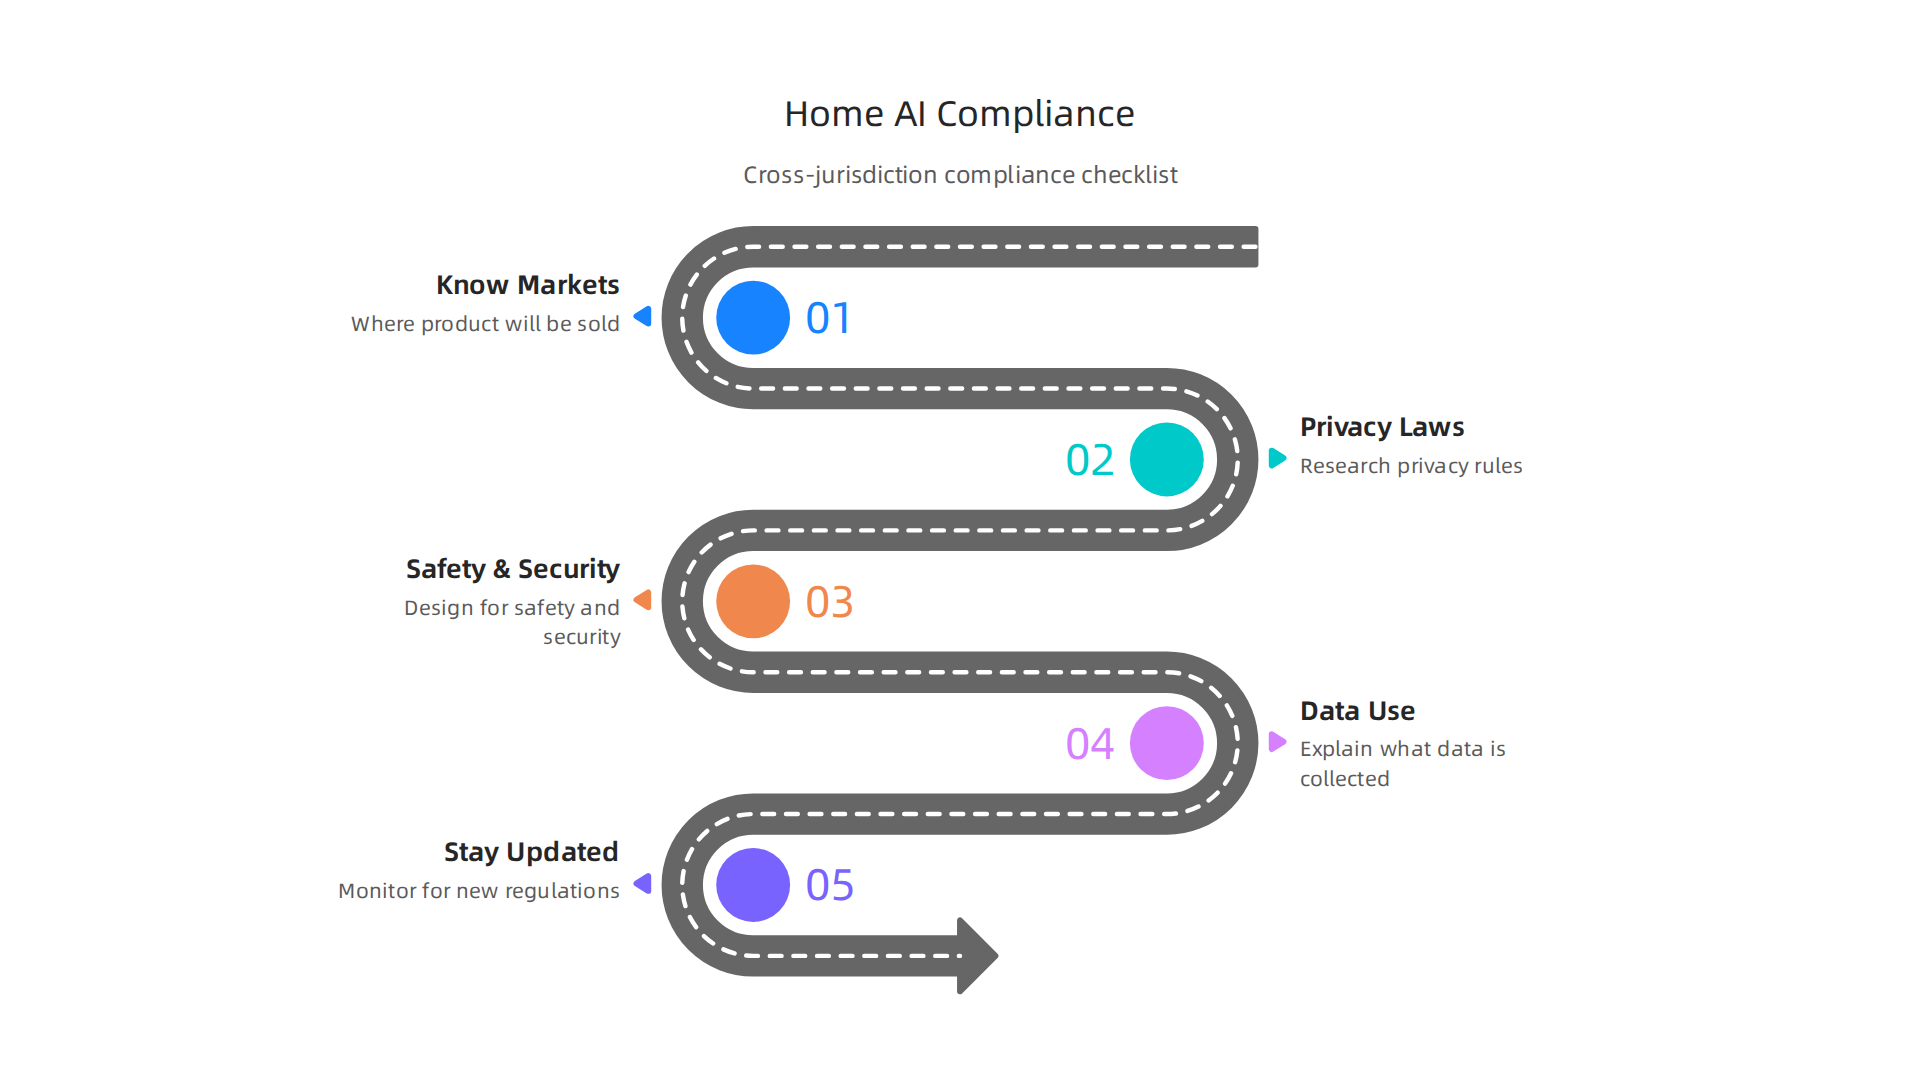
- Know Your Markets: Figure out exactly where your smart home AI product will be sold. Rules are different in the US, Europe, Australia, and other regions.
- Understand Privacy Laws for Each Place: Research the specific privacy rules for data collection and use in every country you plan to sell in. This is a must for any smart device.
- Prioritize Product Safety and Security: Design your products from the start to be very safe and secure against cyber threats. Always follow the latest security standards. To learn more about building secure AI, check out this guide on how to build AI securely and compliantly.
- Be Clear About Data Use: Make sure users clearly understand what data your AI collects and how it’s used. Always ask for their permission in a simple way.
- Stay Updated: Laws and regulations change often. Have a plan to keep checking for new rules and updates, especially concerning new AI models or agentic AI frameworks.
By following these steps, companies can build trusted home AI products and help us truly reimagine home AI for the future. Staying informed is half the battle when it comes to the fast-moving world of tech policy.
To get clear daily AI updates and understand how these policies impact technology, consider subscribing to The AI Newsletter Worth Reading.
We just talked about how staying informed on policy helps make home AI trustworthy and safe. Now, let’s think about taking those helpful AI features we enjoy at home and bringing them into our workplaces. This means we need to truly reimagine home AI for business use. Think about voice assistants, smart schedules, and personalized tools. Companies want to use these kinds of AI features to make work easier and more productive.
For example, imagine using a voice assistant to quickly find a file or schedule a meeting. Or having personalized AI tools like slack ai or chatsonic ai help with everyday tasks or even act as the best ai for research for your team. These ideas sound great, but bringing consumer-style AI into a company setting means we need special rules and careful planning.
Unique Challenges for Enterprise AI
When consumer AI moves to the workplace, the stakes get much higher. Here are some key challenges businesses face:
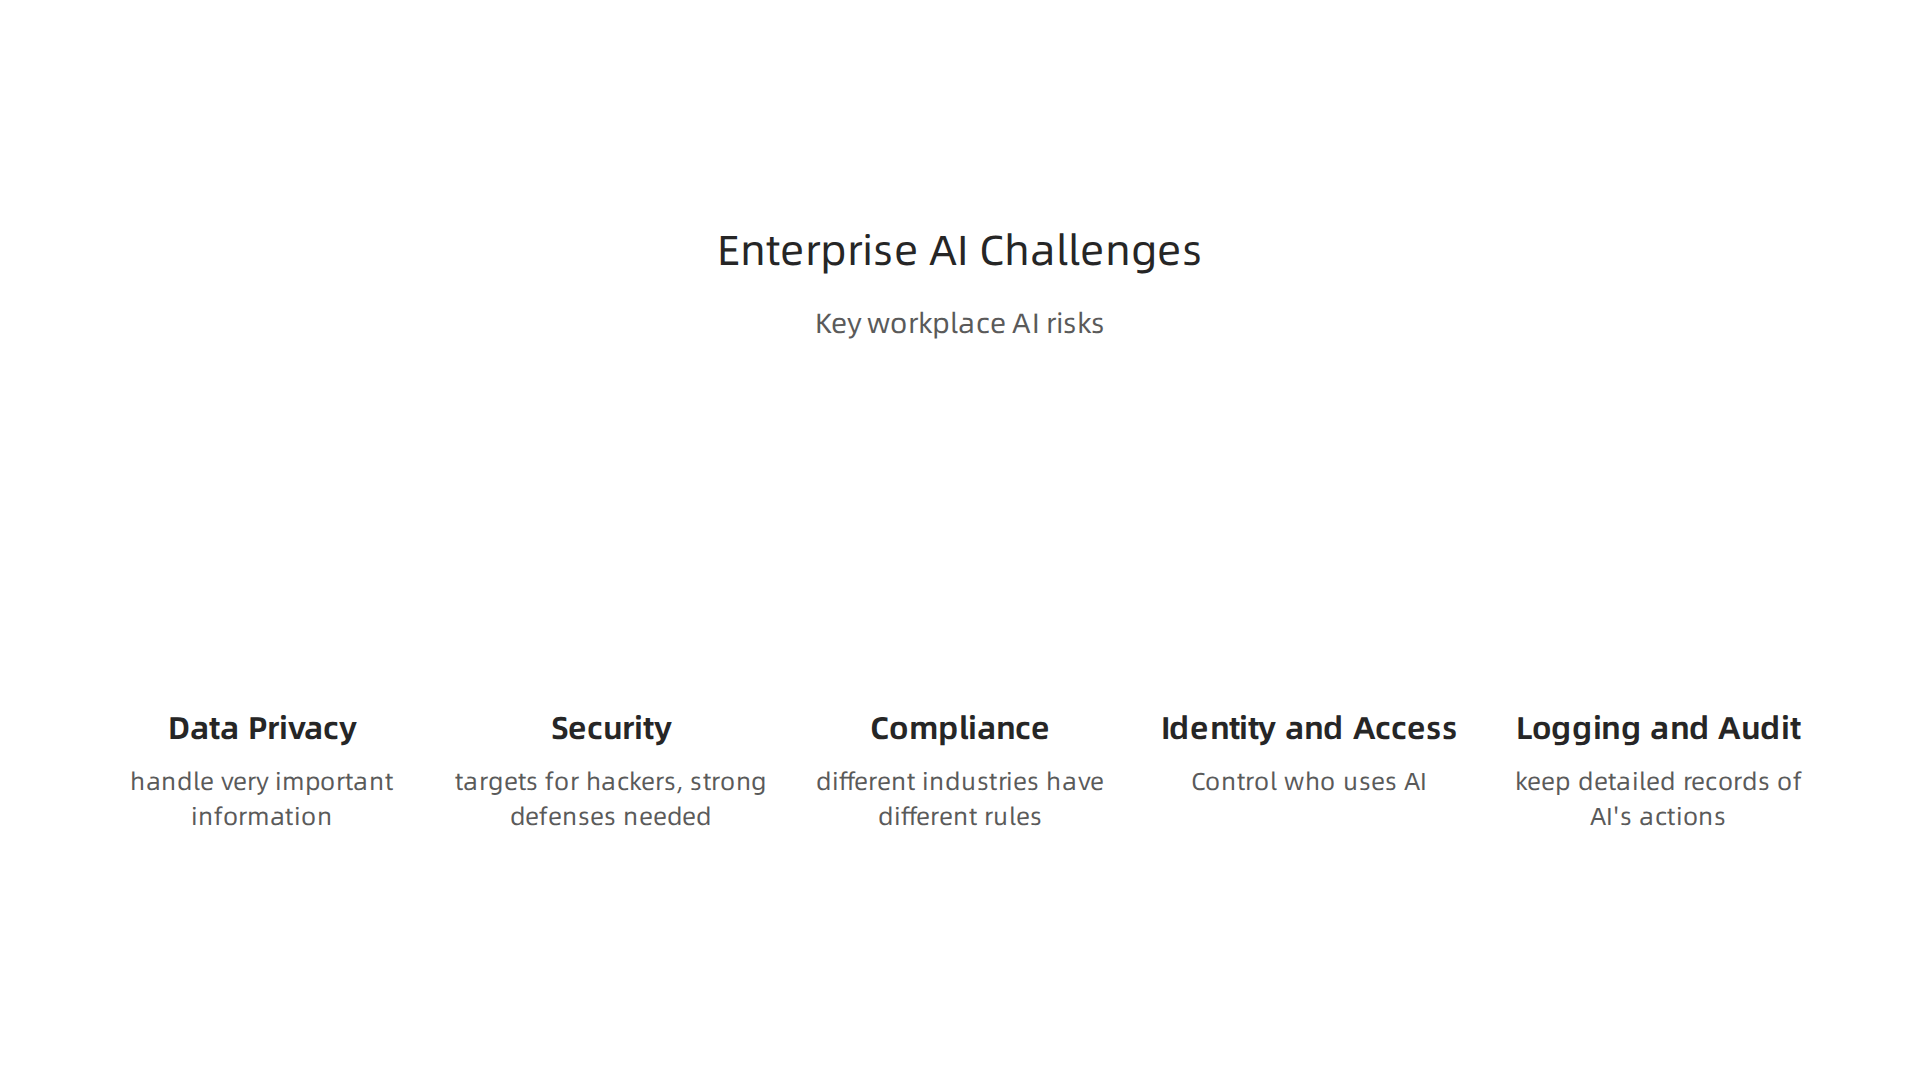
- Data Privacy: In a company, AI might handle very important information, like customer data or trade secrets. Protecting this data is super critical. Companies need to make sure the AI does not share private info by mistake or allow unauthorized access.
- Security: Smart devices and AI can be targets for hackers. In a business, a security breach could be very damaging. So, it is important to build these systems with strong defenses from the start. Guidelines like those from NIST, which help manufacturers make secure IoT products, are very useful here. For instance, the NISTIR 8259 Series offers foundational activities for secure IoT product creation, which applies well to enterprise AI. There are also specific guidelines for federal government use of IoT product cybersecurity, like the IoT Product Cybersecurity Guidelines.
- Compliance: Different industries have different rules. A healthcare company using AI, for instance, has different privacy requirements than a marketing firm. The AI systems must follow all these specific laws.
- Identity and Access Models: Who can use the AI? What information can they access? Businesses need clear ways to control who gets to use AI features and what they are allowed to do. This helps keep company data safe.
- Logging and Audit Expectations: If something goes wrong with an AI, companies need to know what happened, when, and how. This means keeping detailed records of the AI’s actions. Having a good system for AI incident management is vital. Organizations should have an AI Incident Response Framework ready, complete with roles and steps for handling problems. There are even patterns for AI Incident Management that define how to detect, fix, and review incidents.
Securing Enterprise AI Deployments
To make sure these powerful AI tools help rather than harm, companies need to set up strong ways to manage them.
- Clear Use Policies: Companies must create simple rules for how employees can use AI. This includes what type of information can be shared with an AI and what tasks it can perform.
- Robust Security Measures: Building security directly into AI systems is a must. This protects against cyber threats and keeps sensitive data safe. You can learn more about managing risks and innovation by checking out our guide on Open Source AI.
- Incident Response Plans: Even with the best plans, problems can happen. Companies need a clear step-by-step plan for what to do if an AI system acts unexpectedly or faces a security issue. This includes knowing how to quickly find and fix the problem. AI incident response playbooks can help teams be prepared for these situations, offering guidance and strategies for handling everything from bias to data leakage issues, as outlined by AI Incident Response Playbooks.
- Training for Employees: Everyone who uses AI in the workplace needs to understand how it works, what its limits are, and how to use it safely.
As we see more advanced AI systems, including agentic ai frameworks that can act on their own, these governance steps become even more important. By carefully planning and setting up the right controls, businesses can safely bring the power of AI into their operations and truly reimagine how work gets done. For a deeper dive into the world of autonomous agents and their implications, explore our article on AI Agents Explained.
Following our look at making AI safe for businesses, let’s talk about the specific dangers to AI devices. This includes smart gadgets in your home and powerful AI tools used by companies in places like factories or branch offices. These are often called "edge devices." To truly reimagine home ai for wider use, we must understand the risks and how to manage them.
Safety, robustness, and cybersecurity for in-home AI and enterprise edge devices
When we talk about making AI safe and strong, especially for devices that are not big servers but smaller tools at home or at the edge of a company’s network, we need to think about unique dangers. These dangers can come from where the devices are made or even from someone far away trying to control them.
Understanding the Dangers (Threat Models)
Here are some ways AI devices can be at risk:
- Risks from the Start (Supply Chain): Imagine buying a new smart gadget for your home or office, but a hidden flaw was put into it during manufacturing. This is called a supply chain risk. It means bad software or weak security could be built into a device before it even reaches you. This highlights how important it is to trust every step of how a product is made and shipped.
- Taking Control from Afar (Remote Code Risks): Another big danger is when hackers try to take over a device from a distance. They might send bad computer code that tricks the device into doing what they want. This can happen if a device’s software is old or has weak spots that hackers know about. This is especially tricky with
agentic ai frameworks, which are AI systems that can act on their own, because a hacker could make them do harmful things. The NIST Cybersecurity for IoT Program works on helping keep these kinds of devices safe.
Making AI Systems Stronger and Safer
To protect these AI tools and devices, we need clear steps throughout their entire life.
- Careful Testing: Before any AI tool or device is used widely, it needs lots of testing. This helps find and fix problems early, like mistakes the AI might make or ways it could be attacked. Good testing makes sure the AI works as it should, without causing new problems. It also helps ensure the AI meets important safety rules, with clear Requirements and Verification Standards for Artificial Intelligence in Safety-Critical Applications. For more detailed steps, you can learn how to How to Build AI Securely and Compliantly.
- Being Ready for Problems (Incident Response): What if something still goes wrong? Companies need a clear plan for what to do. This is an "incident response" plan. It tells everyone what steps to take if an AI system has a problem, such as a security breach or acting strangely. This plan helps teams fix issues quickly and learn from them. The GenAI Incident Response Guide offers helpful steps for these situations, especially for generative AI. Being ready to respond quickly is key, and good AI Agent Governance can make a big difference.
- Keeping Devices Safe Over Time (Product Lifecycle Practices): AI devices need ongoing care, not just a one-time setup. This means regular updates for software and security. It is like getting updates for your phone or computer. These updates help protect against new threats and keep the AI working well for its whole life. It is also important for
AI Infrastructure 2026to have these strong safety measures built in, always adapting to new challenges. Understanding How Security Teams Should Prepare for AI Incident Data Sharing is also vital for staying ahead of new problems.
By following these practices, businesses and individuals can make sure their AI tools are not only smart and helpful but also safe and secure for years to come.
Want to stay on top of the latest AI trends and policy? Get clear daily AI updates.
The AI Newsletter Worth Reading
After looking at how to make AI devices strong and safe, we must also think about the people who use them. For AI in homes and businesses to truly succeed, people need to trust it, find it easy to use, and feel comfortable with what it does.
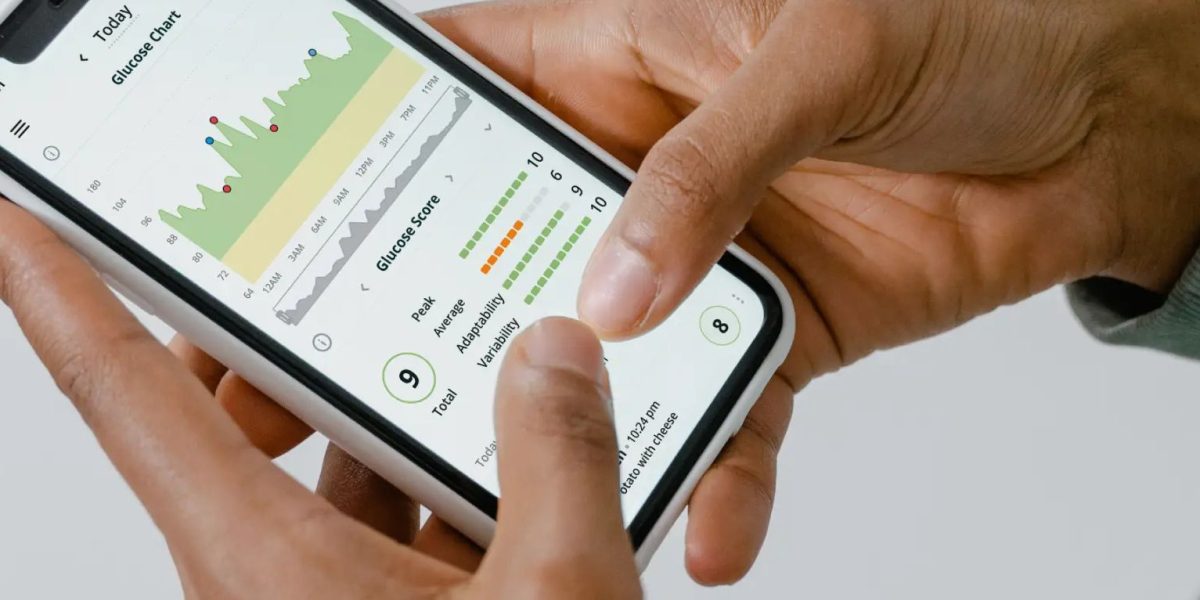
This means we need to reimagine home ai not just as a piece of tech, but as something that fits smoothly into daily life.
User experience, trust, and accessibility: designing home AI that people accept
When AI tools are used every day, like smart home devices or helpful AI assistants at work, their success isn’t just about how smart they are. It is also about how well they connect with people. If people do not understand an AI, or if they feel it is too nosy, they will not want to use it. This is why good design for user experience, building trust, and making AI easy for everyone to use is so important.
Making AI Easy to Understand and Trust
For people to trust AI, they need to know what it is doing and why.
- Be Clear About AI (Transparency): Imagine an AI helping you write an email. You should know it is an AI, not a person. Designers must make it clear when AI is involved, especially in conversations or when it creates something new. This helps people feel respected and in control, avoiding confusion about whether they are talking to a bot or a person Design Disclosure, Consent and Data-Provenance UX.
- Ask Permission (Consent): AI often uses your data to learn and help you better. But it should always ask you first. This is called consent. Good AI design lets you choose what data to share and how it is used. For example, a device might ask for your "audible consent" before it records voices around it AI UX Patterns | Consent | ShapeofAI.com. This should be done simply, giving you clear choices like "Accept all" or "Save preferences" for your data Design a Granular Consent System Users Trust. The best way to do this is to explain things a little at a time, right when you need to make a choice, which is known as Progressive Consent & Communication (PCC). This way, you do not get overwhelmed with too much information at once.
- Explain How it Works (Explainability): Sometimes, AI makes a decision that affects you. It is important for the AI to be able to explain how it came to that decision, especially in serious situations. This helps you understand and accept the AI’s actions, building more trust. This is a key part of
new human ai interaction guidelines for policy professionals and executives.
Designing for Everyone (Accessibility)
An AI that is easy to use for some people but hard for others won’t be widely accepted. To truly reimagine home ai and make it useful for all, it must be accessible. This means:
- Simple Interfaces: Buttons should be easy to see and press, and instructions should be in plain language.
- Different Ways to Interact: Some people might prefer to talk to AI, others might want to type, and some might need visual cues. Offering different ways to interact means more people can use the AI. Think about how tools like
slack aiorchatsonic aitry to make their help available through different modes.
Giving You Control (Balancing Personalization)
AI can be very helpful when it learns your habits and makes suggestions. This is called personalization. But you should always feel like you are in charge.
- Easy-to-Find Settings: You should be able to easily change how much data your AI uses, how much it personalizes things for you, and whether it makes its own choices or always asks you first. For example, with
agentic ai frameworksthat can act on their own, clear controls are vital. - "Off" Switches: Sometimes, you just want the AI to stop. There should always be clear ways to pause or turn off AI features. This kind of user control reduces worries and helps more people feel comfortable bringing AI into their homes and workplaces.
By putting people first in how AI is designed and used, we can build a future where AI is not just smart and secure, but also genuinely helpful and trusted by everyone.
Want to stay on top of the latest AI trends and policy? Get clear daily AI updates.
The AI Newsletter Worth Reading
After looking at how to make AI devices strong and safe, we must also think about the people who use them. For AI in homes and businesses to truly succeed, people need to trust it, find it easy to use, and feel comfortable with what it does. This means we need to reimagine home AI not just as a piece of tech, but as something that fits smoothly into daily life.
Business models, procurement, and liability: commercial realities when you reimagine home AI
When companies decide to use or sell AI for homes or businesses, they face important questions about money, buying, and who is responsible if something goes wrong. If we truly want to reimagine home ai, these business parts must be as clear as the tech itself.
How Companies Make Money with Home AI
Many ways exist for companies to earn from home AI. Some might sell the device itself, like a smart speaker. Others might offer special features that you pay for each month. A big area for making money is using the data that AI collects. For example, your smart home AI might learn your favorite foods and then suggest recipes or even order groceries for you. This kind of personalization can be very helpful, but it also means companies are using your information.
However, using personal data comes with risks. Companies need to be careful about privacy and follow laws. If they are not, people might lose trust, and this can hurt their business in the long run.
Who Is Responsible When AI Makes a Mistake? (Liability)
This is a tricky part. Imagine your smart home AI accidentally orders too much food or changes your thermostat settings to be too hot. Who is to blame? Is it the company that made the AI, the company that sold it, or you for using it?
In 2026, companies that make AI systems often try to limit how much they are responsible for if their AI makes a mistake. They do this by putting special rules in their contracts Technology Sourcing Laws and Regulations Report 2025 – 2026 01 Sourcing AI Solutions. For example, a contract might say the AI maker is only responsible for a small amount of money, like a few months of your subscription fee AI Vendor Contracts: Key Clauses to Demand in 2026. This is much less than what might be common in other types of software contracts Navigating AI Vendor Contracts and the Future of Law. Because of this, buyers of AI systems need to be very careful when signing contracts. They need to make sure the rules about responsibility match the actual risks.
Getting (Procuring) Home AI: What Buyers Need to Know
For businesses wanting to reimagine home ai in their operations, buying AI tools like slack ai or chatsonic ai is more than just picking the smartest one. It means looking closely at how the AI is made, how it handles data, and what the contract says.
For example, the U.S. government has started making new rules for buying AI. These rules would make companies tell the government about all the AI tools they use in a project and make sure their partners also follow the rules GSA AI Procurement Rules Would Introduce New …. This shows how important it is for buyers to be clear on who is responsible for the AI.
A Simple Checklist for Buying Home AI
When a business wants to buy AI capabilities for home-like settings, here’s a simple checklist to help:
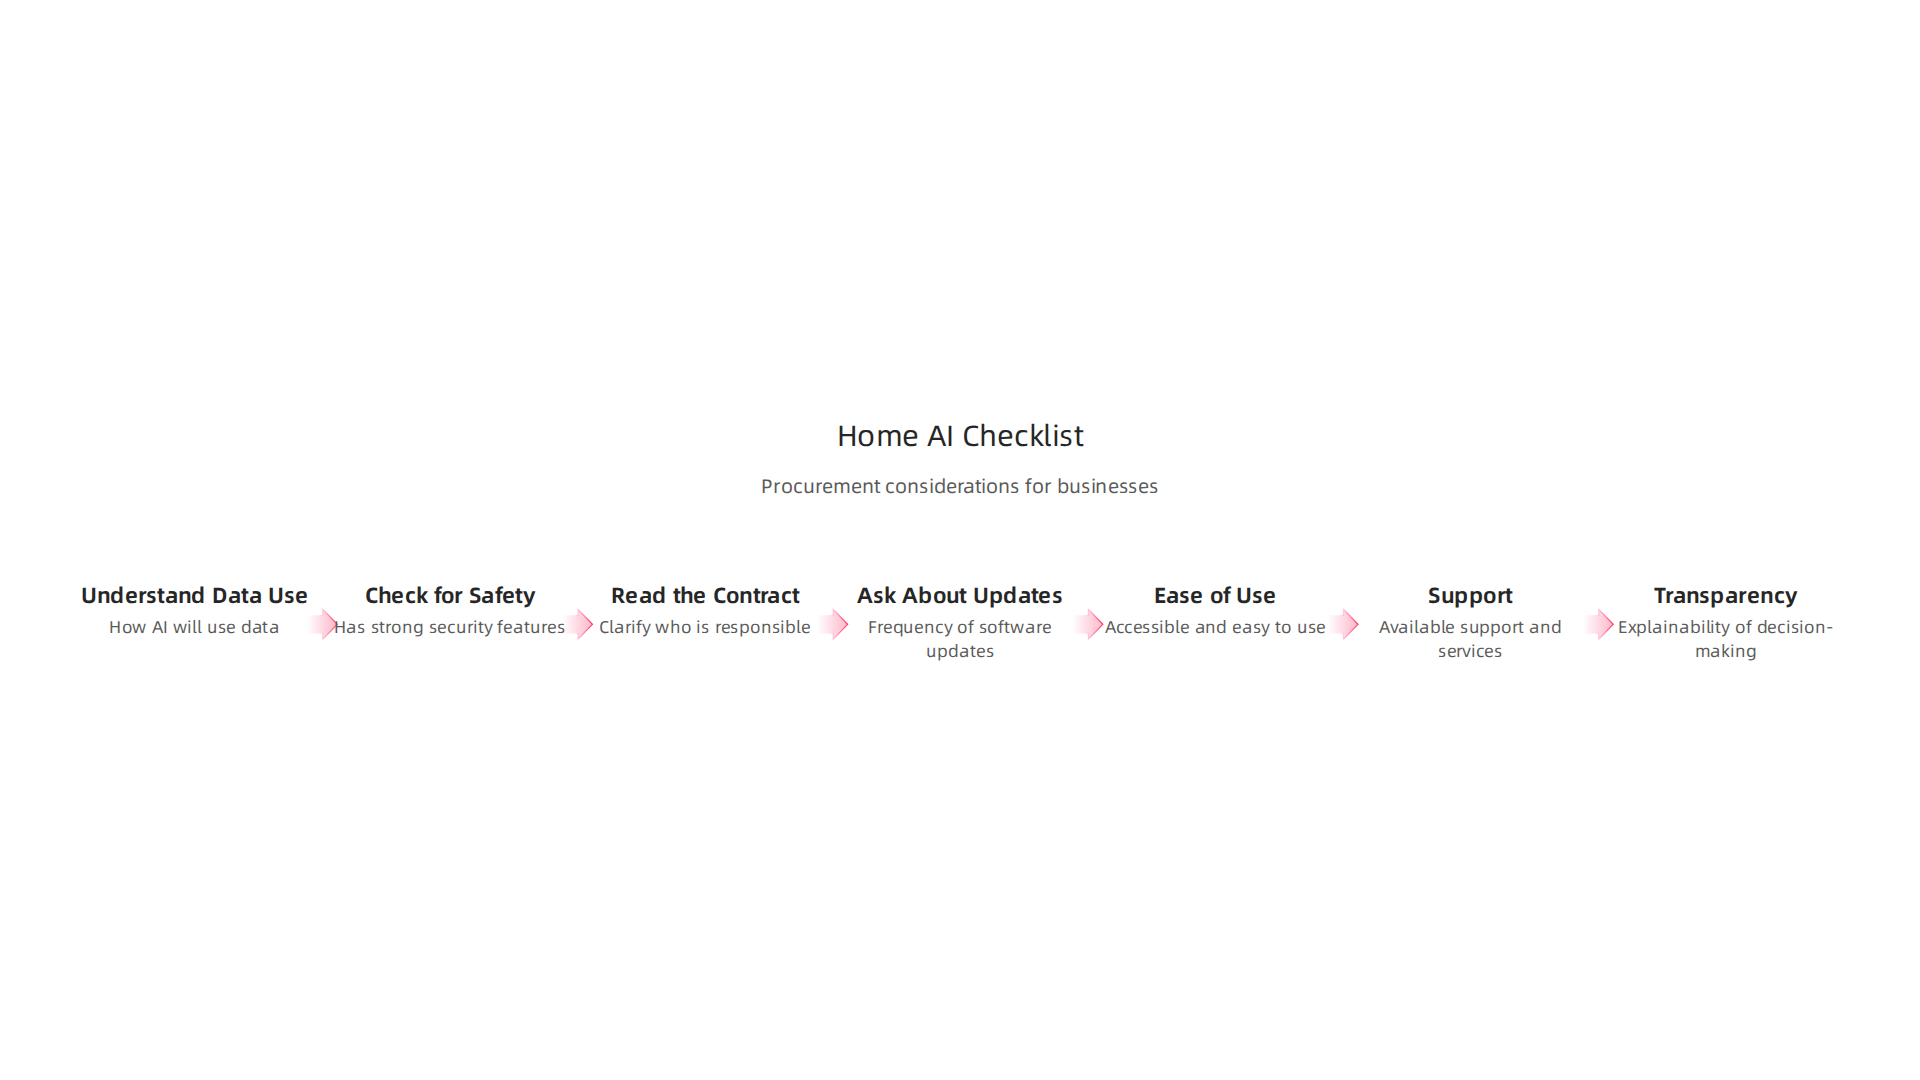
- Understand Data Use: How will the AI use your data? Can you control it? Make sure the company is clear about this.
- Check for Safety: Does the AI have good security features to protect your information?
- Read the Contract Carefully: Pay close attention to who is responsible if the AI makes a mistake or causes problems. Look for "liability caps," which limit how much a company has to pay.
- Ask About Updates: How often will the AI get updates to make it better and safer?
- Ease of Use and Accessibility: Is the AI easy for everyone to use, including people with different needs? This also ties into important legal guidelines like the EU AI Act AI Act And Accessibility: Comply With The Law By 2026.
- Support: What kind of help will you get if something goes wrong?
- Transparency: Can the AI explain how it makes decisions? This is especially important for
agentic ai frameworksthat act on their own.
By asking these questions, buyers can make better choices when investing in AI solutions, whether for smart homes or business tools. This helps ensure they are choosing AI that is not only smart but also trustworthy and reliable. Understanding these business details is key to navigating the big shifts in technology and society, as explored in articles like Cultural and Conceptual Effects of AI Reshape Society.
Want to stay on top of the latest AI trends and policy? Get clear daily AI updates. The AI Newsletter Worth Reading
Summary
This article explains why now is the moment to